Key Points
- An attacker planted skimming code in Optimizely scripts loaded by at least 178 organizations' websites.
- The code swapped crypto wallet addresses, captured card details and served iOS exploit chains to Apple devices.
- Roughly $7,040 in crypto reached the attacker's wallets within about nine hours, Report URI said.
The latest:
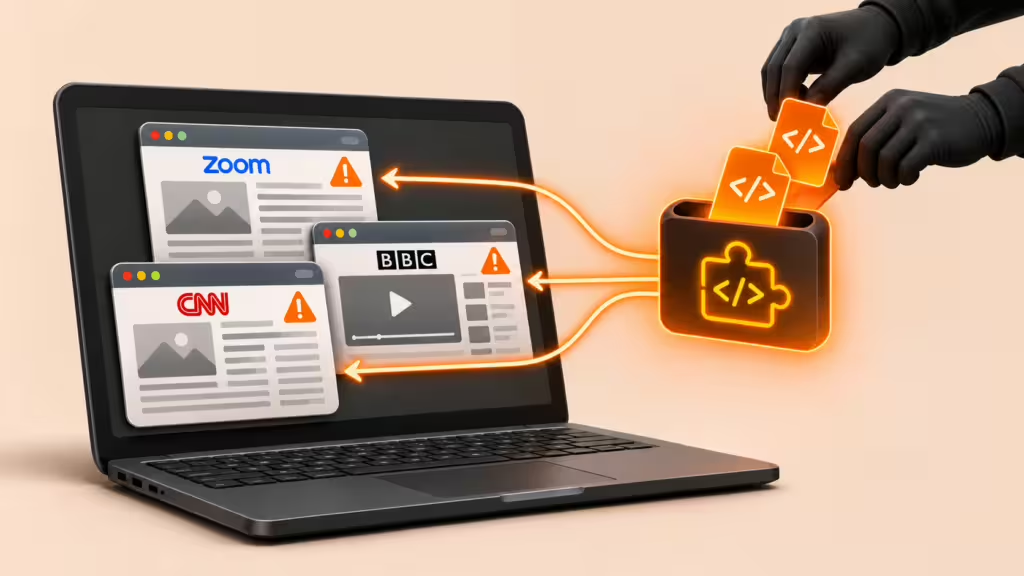
Malicious JavaScript rode into the websites of at least 178 organizations, among them CNN, the BBC and Zoom, through hijacked Optimizely Web Experimentation snippets, script-monitoring firm Report URI said. Optimizely said in an incident notice posted at 01:02 UTC that an attacker had exploited a vulnerability in Experimentation to insert the code into some customer projects, and that it has since fixed the flaw and removed the code.
Details:
- How it worked: The attacker wrote a loader into the Project JavaScript field of customer projects and left the rest of each snippet untouched, according to Report URI. Snippets were still served from cdn.optimizely.com under the vendor’s own certificate, so every page that loaded one also ran the loader.
- Three variants: Most snippets fetched 1688360[.]cc/track.js directly, Report URI said. One version hid that address in base64 so a text search for the domain would miss it; another carried a full copy of the payload that executes if the domain is blocked. Sites serving the snippet from their own domain were affected too.
- The crypto swap: The track.js payload replaces valid crypto wallet addresses with the attacker’s in page text, forms, links, the clipboard and outgoing requests. StepSecurity found it swaps only an address that passes its chain’s checksum and sits near a payment word such as wallet, deposit or send.
- The card skimmer: Added at 13:43 UTC, the skimmer captures card number, expiry date and CVV from the site’s own form fields and sends them to the attacker’s server, Report URI said. It cannot read cards entered through a cross-origin payment iframe such as Stripe’s or Adyen’s hosted fields. The firm cannot see how many cards were exposed.
- iOS component: On iPhones and iPads the code loads boot.js from two .icu domains, which reads the iOS version and opens an exploit chain in a hidden iframe: Coruna for iOS 13 to 17, DarkSword for iOS 18, and a separate chain for iOS 26 that so far only collects device details. Report URI reports no iPhones actually taken over.
- Scale and victims: Report URI checked 1,611 Optimizely snippets and found the code in 188, belonging to 178 organizations, adding the real figure is likely higher. Named victims include Salesforce, GitLab, IKEA, HSBC, Equifax, Air France-KLM, Ledger and Peacock. Optimizely’s own main site and login page also carried the code.
- The timeline: The first injection appeared at 04:21 UTC Monday in the BBC’s snippet and loaded webshell[.]lol, which Report URI calls the same actor’s injector. A mass cleanup began around 20:40 UTC, and by 21:52 UTC only TalkTalk’s snippet still carried the code. The injector first appeared on Turkish sites on September 17.
- Conflicting totals: Report URI said the attacker’s wallets had received about $7,040 as of 19:25 UTC Monday, all within roughly nine hours. StepSecurity put the total across the same addresses at about $6,600, noting two were already in use before the injections and that the chain does not show which transfers came from victims.
- Reinfection signal: Smartsheet’s script was cleaned once and then re-infected with a hidden version of the code, which Report URI said indicates the attacker still had access at that point. Cynet, whose endpoint detection flagged browser connections to the attacker’s server, captured the code on CNN and Zoom pages.
- What Optimizely left out: The vendor’s notice does not say how the flaw worked, how many projects were altered, when the fix was deployed, whether the attacker retains access, or what customers should do. Optimizely said it secured affected accounts and added protections against unauthorized code delivery.
Background:
Optimizely customers embed a vendor-hosted snippet to run page experiments. The snippet refreshes whenever a customer changes a setting and executes a custom code field called Project JavaScript on every load, according to the vendor’s documentation — the field the attacker used.
Between the lines:
Trust in the delivery host is the core problem: because the loader shipped from cdn.optimizely.com under the vendor’s certificate, allow-listing that domain in a Content Security Policy offered no protection, as Report URI noted. Cynet’s researchers describe the iOS activity as conditional delivery, “not a successful compromise of a physical iPhone or iPad,” and caution that a site serving the code was not necessarily itself breached.
What’s next
Watch whether Optimizely discloses how the vulnerability was exploited and which project IDs were altered. Report URI said it retained copies of every infected snippet with hashes and timestamps and could share them with affected organizations and national CERTs.